
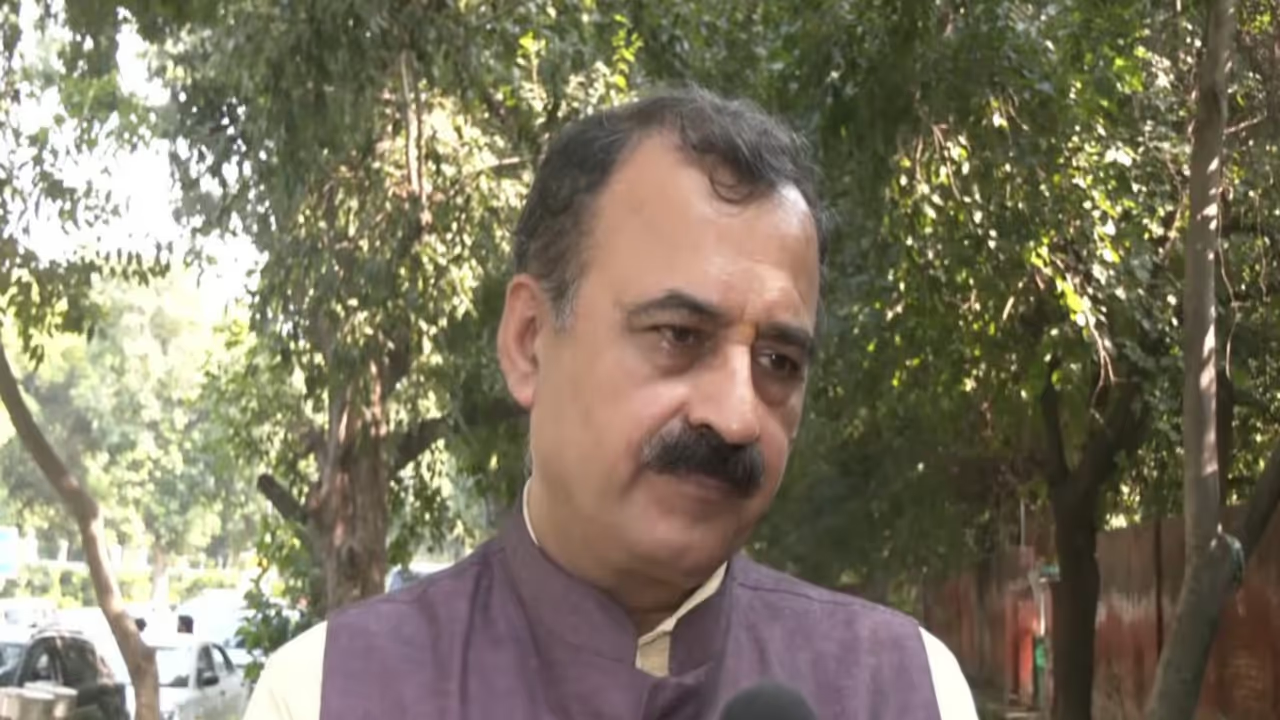
Cybersecurity expert Pavan Duggal urges caution with personal data following the eMudhra incident. He advises a need-to-know approach, independent verification of electronic info, and not assuming data is safe just because it's with the government.
You Are the Custodian of Your Own Data
Duggal, in an exclusive conversation with ANI, said people should not assume that their personal information is automatically safe simply because it is held by government agencies or other institutions. He emphasised the need for greater awareness about how personal data is shared and used in the digital ecosystem.“We should not assume that protecting all our data is solely the government's responsibility and that the government will protect everything without any action on our part. You are the custodian of your own data, and you need to take steps to protect it at a personal level,” Duggal said, advising people to follow a need-to-know approach when sharing personal information. He also stressed the importance of independently authenticating electronic information rather than trusting it without verification, along with following basic cybersecurity practices.
The eMudhra Security Incident Explained
His remarks come amid concerns over a security incident involving digital signature certificates issued by eMudhra. The company provides digital signature certificates used to authenticate electronic information and support trust in digital transactions and online services. The incident involved the generation of weaker cryptographic keys due to a system error in April 2025. An independent security researcher identified the vulnerability, following which concerns emerged over the possible risks to systems relying on the affected certificates.
Potential Security Risks and Government Scrutiny
Digital signature certificates are used by websites and other systems to establish authenticity. Duggal said systems using affected certificates could face potential security risks, including unauthorised access to websites, servers or computers. Such access could, in turn, expose confidential or banking information. However, these are potential risks and do not establish that the affected systems were hacked or that data was stolen.
Duggal said the government had formed a team under the Ministry of Electronics and Information Technology (MeitY) to examine why weak keys were generated and what steps the company took after becoming aware of the issue. He said investigators need to establish when the company detected the problem, what action it took to limit potential damage and whether it reported the matter to the Indian Computer Emergency Response Team (CERT-In), the country's nodal cybersecurity agency.
Expert Calls for Legal Investigation
The expert also called for a First Information Report (FIR) and a law-enforcement investigation, saying the circumstances surrounding the incident and the company's response needed closer examination. He said “In this case, an FIR should be registered under the relevant provisions of the Bharatiya Nyaya Sanhita as well as the Information Technology Act. Action should be taken against those responsible for any wrongdoing”.
Scope of Impact and UPI Assessment
Duggal also said the potential exposure was not necessarily limited to India, as the risk could extend to systems in other countries using the relevant certificates. At the same time, he noted that not every website, application or user was necessarily affected.
Addressing concerns over digital payments, Duggal said he did not see an immediate risk to the Unified Payments Interface (UPI), as it operates on a different platform and framework. This assessment should not be interpreted as evidence that all digital services are risk-free. (ANI)
(Except for the headline, this story has not been edited by Asianetnews Editorial staff and is published from a syndicated feed.)